Total System Failure: U.S. Government Networks Will Need To Be Torched And Rebuilt
From dodgy DOGE bros to White House systems compromised by foreign intelligence, Trump cybersecurity damage will take decades and untold billions to repair.

Last week a cybersecurity firm named Layer3 Intel quietly announced that they'd found something troubling: numerous Trump administration officials had installed dodgy Russian proxy spyware on their computers at the White House, potentially allowing unauthorized access to U.S. government networks.
This kind of proxy software allows users to mask their IP address, spoof their real location, or "rent" bandwidth for as little as 60 cents a Gigabyte. Often computers are unknowingly infected with such software, then used in massive botnet attacks.
Needless to say, this shouldn't be happening at ordinary companies with competently run IT departments, much less the White House, where you can now apparently access extremely-sensitive government IT networks and secrets for far less than the cost of a cup of coffee.
At least one of the 28 (!) dodgy proxy services found installed on numerous White House computers (Infatica) is linked to a Russian company whose founder’s web hosting business was central to cyberattacks against election systems in Arizona and Illinois in 2016.
According to the firm's analysis, data transfers from the White House using this dodgy software curiously ramps up each day after normal business hours:
Most of the activity happens in the evening, Eastern time: about half of it falls between 5 p.m. and midnight, and almost none happens in the early morning. That pattern suggests a person rather than a public guest Wi-Fi network: someone regularly on the White House network late into the evening, whose device is infected with a proxy SDK.
Definitely nothing sketchy about that, right? Major news outlets, many of the same organizations obsessed with Hillary Clinton's email scandal during the 2016 Presidential election, so far haven't deemed this a story worth covering.
Of course this is just one small story in a sea of evidence that the Trump administration is not only personally clownish on cybersecurity, but has enthusiastically dismantled numerous government organizations tasked with ensuring Americans are protected from bad actors, both foreign and domestic.
Last year you might recall that Elon Musk and his data-stealing DOGE bros had been caught installing unauthorized Starlink satellite terminals on the roof of the White House and the neighboring Eisenhower Executive Office Building.
At the time, the Secret Service told the Washington Post that this was ok because Musk, everybody's favorite white supremacist fake engineer, was just making White House broadband connectivity better, for free, out of the kindness of his heart:
"We were aware of DOGE’s intentions to improve internet access on the campus and did not consider this matter a security incident or security breach.”
He's a supergenius rocket scientist! Why would people tasked with defending government integrity adhere to basic, long-tested security standards?
The White House is awash with highly-secured, multi-gigabit Ethernet and Wi-Fi connectivity. There's simply no reason you'd be installing slower, less secure Starlink satellite systems unless you were looking to engage in off-book communications or steal government data en masse (recall that one DOGE bro was found to have stolen vast troves of social security data using a USB drive).
At the time, Musk and Trump lied, claiming that Musk was simply donating Starlink connectivity for altruistic reasons. Amusingly, a Washington Post report this week revealed this was also bullshit, and taxpayers have been footing the bill for this lazy-ass hack job the whole time:
"...contracting records reveal that the Trump administration has been spending taxpayers’ dollars since last year to install and service Starlink equipment at the White House. In four contract awards from March 2025 to June this year, the government has agreed to pay nearly $1.2 million to SpaceX for services provided to the White House Communications Agency, a military unit that sets up secure communications for the president, vice president and other officials."
So in short you, the taxpayer, paid the world's richest man to install dodgy, potentially unencrypted satellite terminals on the roof of government buildings, to obscure their dodgy dismantling of the federal government and wholesale theft of sensitive data. Under the pretense of government efficiency, no less.
You'd like to think that Democrats will treat this as an investigative priority in the new year under our reconstituted Congress, resulting in a flood of subpoenas.
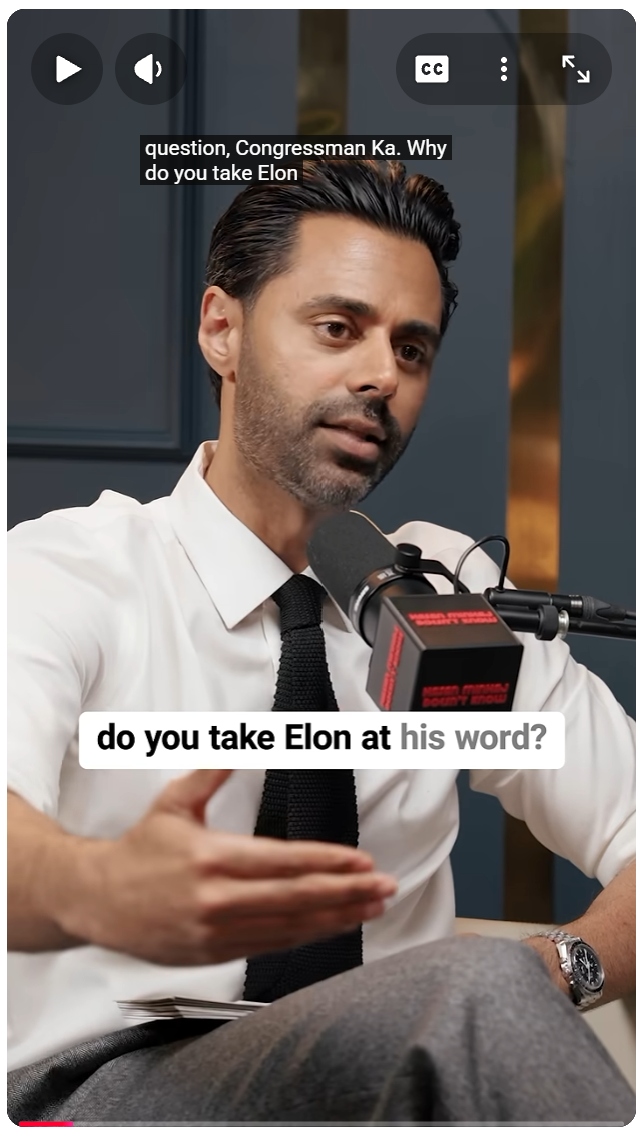
Though it's important to remember that last year, countless Democratic lawmakers, like California Rep. Ro Khanna, implied that DOGE was a legitimate government efficiency effort that Democrats should be cooperating with. This was an amazing exchange from last year (with a hat tip to yours truly):
This is still just a tiny fraction of the cybersecurity bullshit going on within the most corrupt and incompetent administration in U.S. history.
There was also the massive Salt Typhoon hack, where Chinese-government linked hackers gained historic access to nearly every major U.S. telecom network in order to spy on government officials. The intrusion was so total, most telecoms are still struggling to fully understand just how compromised our networks are.
At one point Comcast lawyers told their network engineers to stop looking for evidence of intrusion for fear of liability. Last year, the Trump administration shut down the Cyber Safety Review Board tasked with protecting U.S. IT cybersecurity and investigating the width and breadth of the Salt Typhoon hack.
The Trump administration has not only disemboweled our cybersecurity (and labor, consumer protection, and environmental) regulators, it has undermined efforts to rein in privacy abuses by corporations and data brokers, encouraging international free for all abuse of public location, browsing, driving, and other data by dodgy companies and foreign intelligence alike.
I've noted repeatedly in my writing that the Trump administration's cybersecurity policy has been indistinguishable from a foreign attack. It's also impossible to determine where the incompetence ends and the malicious corruption starts.
Trump, and his administration, have consistently been found to be using unsecured personal phones and private software email services. As a result, they've been trivial for foreign governments to hack (see this story on Jared Kushner's phone being hacked, revealing he was taking foreign bribes).
Because they're too ignorant, corrupt, and victictive to believe in having a functional federal government, they don't put much stock in stuff like multi-factor authentication (MFA) or Common Access Cards (CAC) / PIV verification. And they haven't much cared for the kind of strict Defense Information Systems Agency (DISA) and Secret Service controls required to maintain IT integrity.
You'd have to also assume they didn't follow coherent IT security or hiring standards when building the new ballroom, potentially opening the door to a foreign and domestic surveillance bonanza.
There's endless stories about how Trump and his allies are extremely low-hanging fruit for foreign intelligence, culminating in last week's revelation that Trump BFF and NVIDIA CEO Jensen Huang (who has intimately helped Trump coordinate his "AI policies") has been having an affair with a Chinese spy:
Huang’s [tech industry and Republican] defenders framed his affair as a personal lapse in judgment rather than evidence of treachery against the United States, which has imposed strict limits on what chips Nvidia can sell to China.
Indeed.
This is before you even get to Trump illegally storing classified documents in his personal bathroom, or the countless other examples of administration corruption, incompetence, and greed running roughshod over national security.
Layered on top of that is an absurdist performance by the broken U.S. press, where the Trump administration's bumbling, self-serving tech policies are routinely normalized and sanewashed as good faith efforts to protect U.S. consumers.
So with one hand the administration is engaged in clumsy protectionist efforts to ban cheaper Chinese EVs, drones, roombas, and TikTok in order to "protect American national security and privacy," while with the other ensuring that Russian, Israeli, Iranian, and Chinese intelligence have unfettered access to our dirtiest laundry.
Needless to say, the Trump administration's dangerous cybersecurity buffoonery – from dodgy DOGE tweens to compromised IT systems – should be a very fertile area for Democratic investigations in the new year under a reconstituted Congress if they're truly interested in doing their jobs correctly.
It should be assumed that all the dodgy cybersecurity shit we've seen to date is just the very tip of a very large iceberg. I don't think the full scope of the damage – or how long it will take to repair – is even fathomable at this point.
Until then, U.S. government IT infrastructure should probably be considered completely compromised by foreign actors. Fixing it will require a total audit and rebuild that will be going on long after Trump is dead. You will, of course, also be footing the bill for that. With much of that money going to the same tech companies that personally helped bring Trump to power in the first place.